About
A founder-led practice, built on enterprise operating experience
PRINEXIS is an advisory firm, not a managed service provider. We bring senior judgment, technical depth, and independence to organizations that need enterprise-level capability without enterprise consulting complexity.
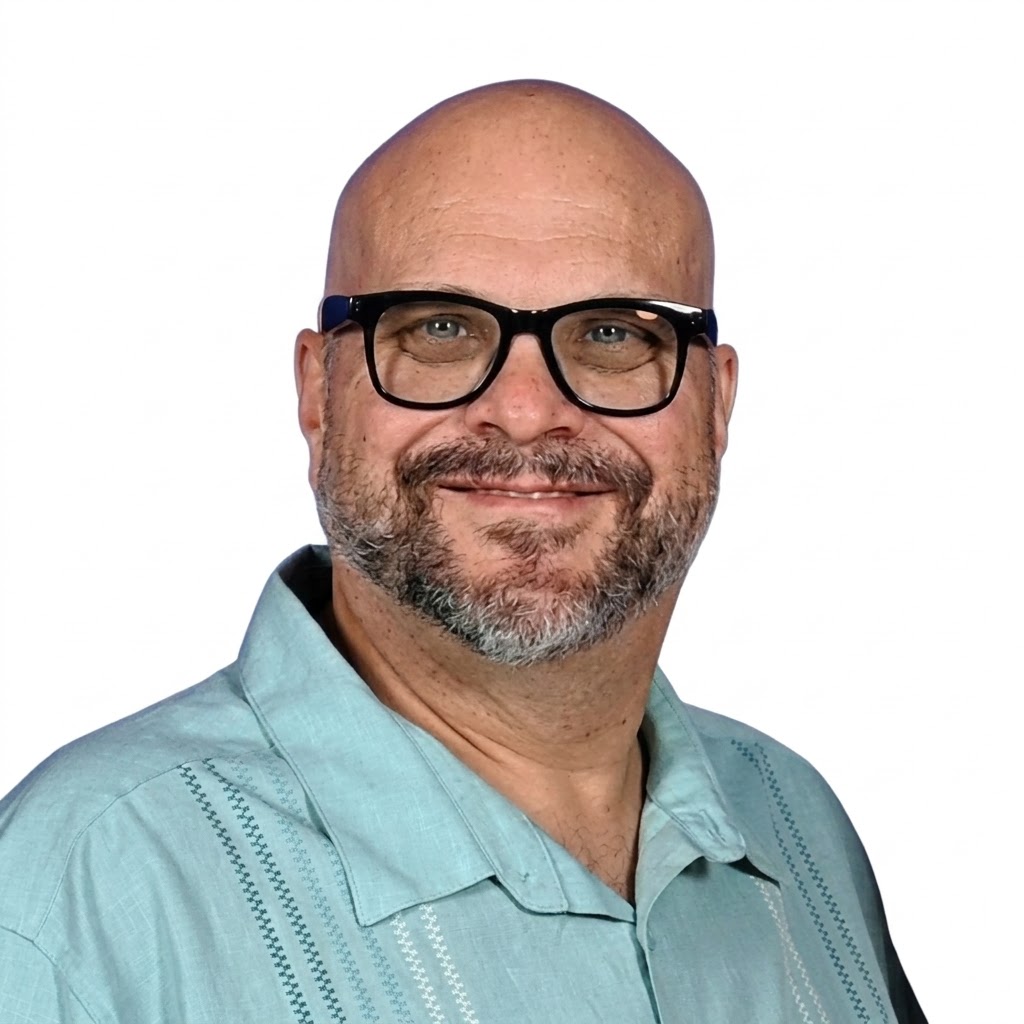
Eric Stermer
Founder & Principal Consultant
Eric Stermer brings three decades of technology experience, including more than 25 years leading enterprise infrastructure, cybersecurity, governance, and technology operations across complex, international, multi-location organizations. His experience combines executive technology leadership with hands-on work in security, compliance, infrastructure, operational technology, team development, and organizational change.
Eric also has a professional background in education and earned a California Designated Subjects Vocational Education Teaching Credential: Full Time. This experience informs PRINEXIS's practical approach to workforce development, executive education, IT team mentoring, and translating complex requirements into programs people can understand and apply.
He works across the full range of stakeholders a technology decision touches — executives, boards, auditors, technical teams, and vendors — translating between business priorities and technical reality in both directions.
Operating Principles
How we approach every engagement
- Security first, with risk explained in business terms.
- Compliance as a management framework, not a paperwork exercise.
- Reliable, maintainable solutions over unnecessary complexity.
- Independent recommendations based on client needs, not resale incentives.
- Business alignment and total cost considered in every recommendation.
- Advice calibrated to the client's people, resources, and operating reality.
Sectors Served
Manufacturing and international multi-site operations are our strongest demonstrated credibility anchors — the same capabilities transfer across distribution, SaaS, construction, civil engineering, real estate, property management, education, and professional services.
A Note on Scope
What PRINEXIS is — and isn't
PRINEXIS is
- A founder-led IT leadership and cybersecurity advisory firm.
- A source of fractional CIO and fractional CISO leadership.
- An independent advisor working from the boardroom to technical architecture.
- A partner for strategy, governance, assessment, team development, education, and complex technology change.
- A practitioner-led firm fluent in international, multi-site, industrial, operational, and regulated environments.
PRINEXIS is not
- A residential support or computer-repair company.
- A commodity managed-service provider or outsourced helpdesk.
- A 24x7 network operations center.
- A staffing company or product reseller whose recommendations depend on licensing or hardware margin.
- A generic training company or theory-only consulting practice.
- A narrowly focused cybersecurity firm — security is central to what we do, not all of it.
Representative Engagements
Illustrative scenarios, not confidential specifics
Composite, anonymized examples of the type of work PRINEXIS does — details are generalized to protect confidential employer and client information.
Building a Reactive IT Team Into a Functional One
Situation: A multi-site manufacturer's IT function was reactive, understaffed, and had no clear roadmap.
Role: Fractional CIO engagement covering organizational assessment, hiring support, and a 12-month roadmap.
Result: A restructured team with clear roles, a prioritized roadmap, and leadership able to sustain it independently.
Turning AI Adoption Into a Governed Program
Situation: Staff across several departments had begun using generative AI tools with no policy or data-handling guidance.
Role: Fractional CISO engagement to assess shadow AI risk and build an acceptable-use and governance program.
Result: A board-approved AI governance policy, an approved-tool list, and role-based staff education.
De-Risking a Multi-Site Acquisition
Situation: A private-equity-backed buyer needed technology due diligence across a target with international locations.
Role: Pre-close IT, security, and licensing due diligence, followed by a post-close integration roadmap.
Result: Technology and security risks identified before close, with a clear integration sequence for identity, network, and controls.
Ready for an independent perspective?
Schedule a consultation to talk through where your organization stands today.